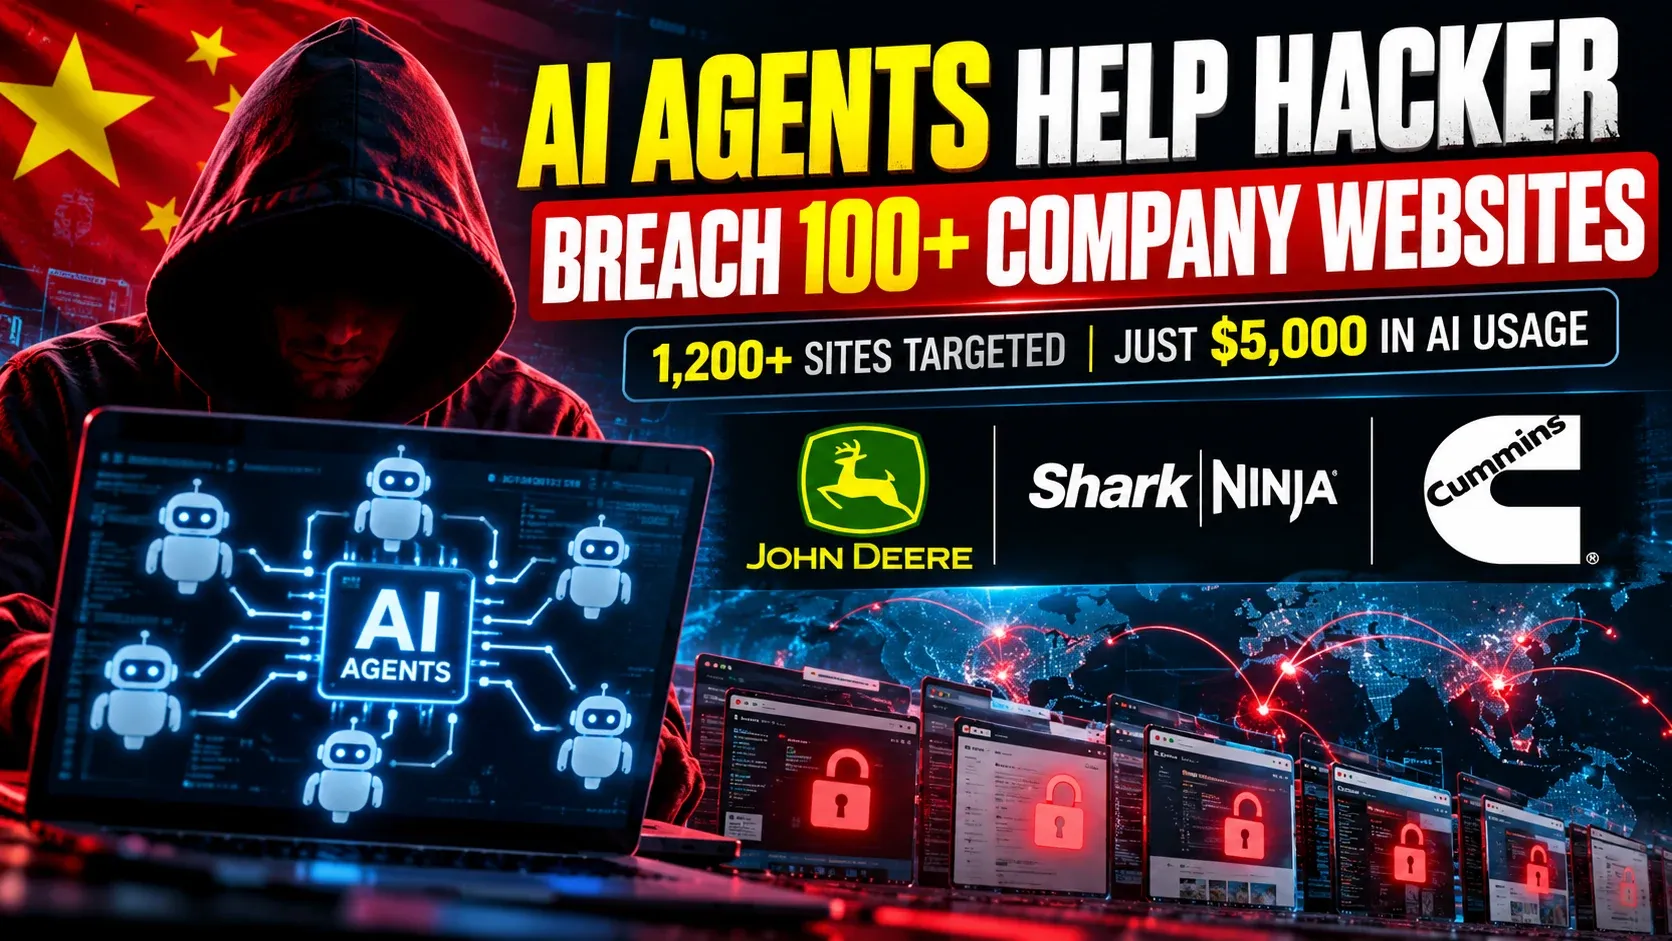
A cyberattack campaign involving artificial intelligence has raised fresh concerns about how quickly attackers can scale their operations. According to reporting published on October 19, 2026, a Chinese-speaking hacker delegated much of a website-intrusion campaign to AI agents, reportedly spending about $5,000 on AI usage.
The agents attempted to compromise more than 1,200 websites and gained access to websites associated with over 100 companies, including businesses in the United States, Canada, Australia and Japan.
How the AI-powered campaign worked
The investigation linked the campaign to Cairn, an open-source AI problem-solving platform. Cybersecurity researcher Snorre Fagerland of NorForge reported finding exposed Cairn instances being used for malicious activity, allowing him to observe parts of the operation.
Instead of manually directing every step, the attacker gave the agents brief instructions and allowed them to spend hours probing websites, searching for weaknesses and attempting intrusions. Successful intrusions reportedly took around 23 hours of automated investigation and activity.
The estimated $5,000 cost refers to AI-token usage, according to the researcher. It is not a complete measure of the campaign’s total cost, nor does it mean every cyberattack can be carried out for the same amount.
Deere, SharkNinja and Cummins among the named companies
The reported targets included farm-equipment manufacturer Deere, home-appliance company SharkNinja and engine maker Cummins.
Companies described different circumstances surrounding the reported activity. Deere said it had no indication that sensitive information was accessed after it took remediation measures. SharkNinja said the affected website was a standalone product-support site and that the threat had been contained. Cummins said it was investigating a report concerning a potential cyberattack on a website operated by a third-party vendor.
The available reporting does not establish that every targeted company suffered data theft. The full extent of any information accessed or taken was not clear.
Why autonomous AI agents change the cybersecurity threat
Traditional cyberattacks often require people to repeatedly research targets, test weaknesses and decide what to try next. AI agents can automate parts of this process, allowing one operator to pursue many targets without having to supervise every action.
This does not mean AI can automatically defeat every security system. The reported campaign demonstrates how automation can make persistent, large-scale probing more accessible, particularly where internet-facing websites have weaknesses or are not adequately monitored.
The same technologies can also support defensive security work, including authorised vulnerability testing, log analysis and incident response. The distinction is whether the systems are being used within permission and appropriate safeguards.
What businesses can do to reduce risk
Security teams should review internet-facing websites and third-party services, patch known vulnerabilities, restrict administrative interfaces, enforce multi-factor authentication and monitor unusual automated activity.
Organisations deploying AI agents internally should also limit their permissions, isolate sensitive systems, log agent actions and require human approval for high-impact operations. Exposed AI control panels and poorly secured automation tools can themselves become entry points for attackers.
The bigger picture
The reported campaign is a warning that AI can reduce the amount of manual effort required to conduct cyber operations at scale. For businesses, the priority is not simply detecting AI use; it is closing exploitable weaknesses, limiting access and identifying suspicious activity before an intrusion escalates.
The case also reinforces an important distinction: the number of websites targeted, the number successfully accessed and the amount of data stolen are separate measures. The reported figures show the scale of the campaign, but the complete impact remains uncertain.